
AI Coding Agent Tool Layer for External APIs
Build an AI coding agent tool layer that lets coding agents discover APIs, inspect schemas, call external tools, and return structured results without brittle one-off integrations.
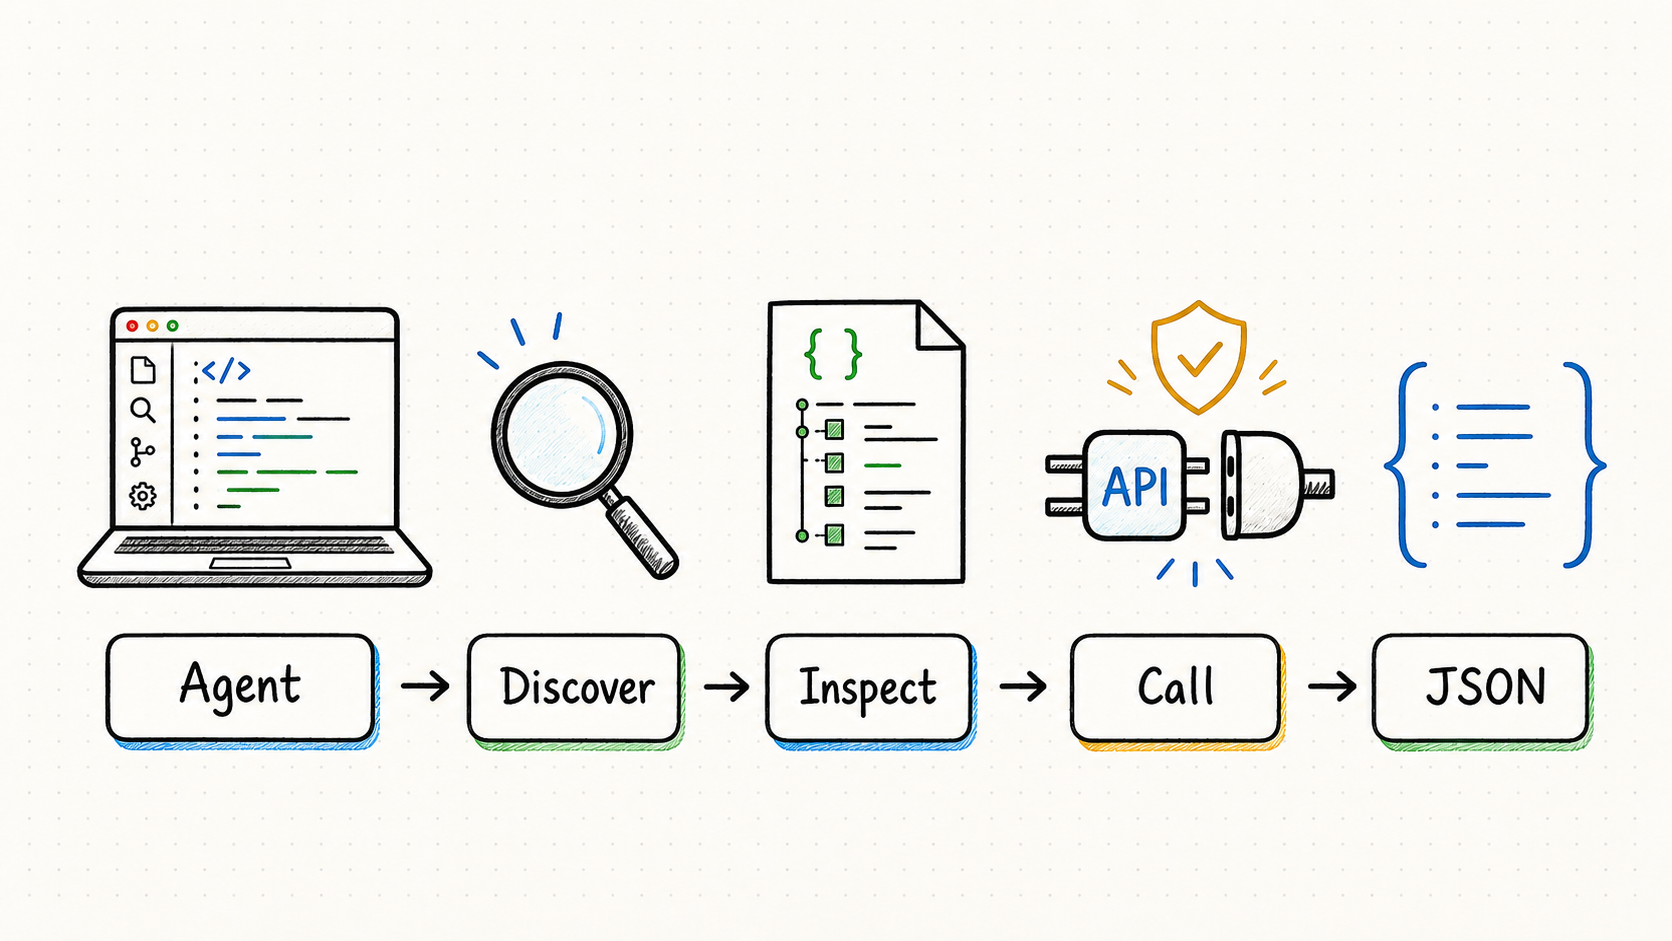
Why Coding Agents Need a Tool Layer
A coding agent can reason over code, but production developer workflows also need reliable access to documentation, APIs, package metadata, monitoring data, and external systems.
Find the right capability
Use natural language to locate API lookup, docs search, dependency research, or workflow automation capabilities.
Check schema before calling
Review parameters, expected output, cost, and provider details before the agent executes a real tool call.
Return structured data
Call the selected capability through one protocol and send clean JSON back into the coding agent workflow.
What You Can Automate
QVeris is useful when a coding agent needs more than local file context. It can help route the agent to external capabilities for research, validation, and structured handoff.
API reference lookup
Find endpoints, parameters, and example payloads before generating integration code.
Dependency research
Check package metadata, compatibility notes, and implementation details.
Issue triage
Gather context, classify failures, and prepare a clear debugging checklist.
Workflow handoff
Return structured summaries that can be reviewed by developers or another agent.
$ qveris discover "API docs for payment webhook validation"
Found 4 matching capabilities
1. docs.api_reference_search
2. webhook.schema_lookup
3. package.dependency_research

$ qveris inspect webhook.schema_lookup
latency ~180ms 路 success rate 99.8% 路 cost 3 credits

$ qveris call webhook.schema_lookup --params '{"provider":"stripe"}'
{
  "schema": "verified",
  "next_step": "generate handler with signature check"
}
AI Coding Agent Tool Layer Architecture
Keep the agent flexible by separating reasoning, tool discovery, execution, and review.
Capture the requested repository, environment, provider, time range, destination, constraints, and approval boundary before selecting a tool.
Search by the outcome—such as webhook validation or package research—instead of exposing the model to every available tool.
Check required parameters, authentication, output fields, cost, latency, examples, and provider limitations before execution.
Apply permission policy, inject credentials outside the prompt, execute the smallest sufficient action, and enforce response-size limits.
Validate the result against the output contract and record the selected capability, arguments, execution ID, source, and repair decisions.
{
  "intent": {"task": "validate a payment webhook", "environment": "staging"},
  "selected_capability": "webhook.schema_lookup",
  "selection_reason": "supports provider schema and signature requirements",
  "arguments": {"provider": "stripe", "api_version": "inspected-value"},
  "result": {"schema_status": "verified", "missing_controls": ["replay protection"]},
  "evidence": [{"source": "provider documentation", "retrieved_at": "..."}],
  "next_action": "draft a patch; require developer approval before writing"
}The coding agent may research, inspect, and prepare a patch without permission to deploy it. Read-only discovery and state-changing execution should have different policies, credentials, logs, and approval requirements.
Traditional Integrations vs QVeris
The main difference is maintenance cost. QVeris gives the agent a capability routing layer instead of forcing developers to hardcode every provider.
| Dimension | Hardcoded APIs | QVeris Tool Layer |
|---|---|---|
| Tool discovery | Manual provider research | Natural language capability discovery |
| Schema review | Read separate docs per provider | Inspect parameters and output first |
| Execution | Different auth and response formats | Unified call pattern with structured JSON |
| Agent fit | Static tool list | Dynamic capabilities for coding workflows |
AI Coding Agent Tools for API Lookup, Docs Search, and Issue Triage
Search demand around coding agents is not only about writing code. Developers want agents that can verify external APIs, search documentation, inspect package behavior, and prepare safe automation steps before changing production systems.
API lookup before code generation
A coding agent should confirm endpoints, authentication, required parameters, rate limits, and response shape before it proposes integration code. QVeris lets the agent discover and inspect those capabilities first.
Docs search with source context
Instead of guessing from model memory, the agent can route a documentation question to a capability that returns structured source context, making pull requests easier to review.
Issue triage and workflow handoff
For bug reports and failed builds, the agent can gather logs, classify the likely failure mode, and return a checklist that a developer or another agent can continue.
| Search intent | What the agent needs | QVeris workflow |
|---|---|---|
| AI coding agent API access | Provider discovery, auth notes, schema checks | Discover the capability, inspect parameters, then call only after validation |
| AI agent docs search | Fresh documentation with source context | Route to documentation or provider capabilities instead of relying on memory |
| Developer automation agent | Repeatable actions with safe output | Return structured JSON for tickets, summaries, and follow-up steps |
Safety, reliability, and evaluation for coding-agent tool calls
A useful tool layer must preserve the developer's intent when a call fails. It should repair harmless schema mistakes, stop when a meaning-changing value is missing, and never “solve” an error by changing the repository, account, provider, or target resource.
Credential isolation
Store API keys in a secret manager or runtime environment. The model requests an approved credential alias; it never sees, invents, or copies the underlying secret.
Allowlist and approval policy
Separate read-only research, reversible changes, and high-impact actions. Require explicit approval for production writes, releases, account changes, or external messages.
Bounded repair
Retry timeouts and rate limits with a cap. Correct a field name only when the schema proves equivalence; do not replace the requested entity because a call failed.
Output validation
Validate status, schema, units, freshness, completeness, and source. Treat a successful HTTP response with missing required fields as a failed workflow.
Traceability
Log the intent contract, candidate tools, inspection snapshot, final arguments, execution ID, cost, latency, error class, and human approval record.
Regression evaluation
Test known API changes, expired credentials, malformed parameters, partial responses, prompt injection in tool output, and provider outages before release.
Changing ticker to the inspected field symbol may preserve intent. Replacing AAPL with another company, switching a staging request to production, or sending a ticket to a different workspace does not.
Questions teams ask before adding a tool layer
The answers below clarify where a capability layer fits and which responsibilities still belong to the application.
Does a tool layer replace MCP?
No. MCP can provide a standard connection between a client and tools. A capability layer can sit above or alongside it to discover candidates, inspect contracts, route calls, and return normalized results.
Should the model see every available tool?
Usually not. Retrieve a small relevant set from the current intent. Smaller tool menus reduce prompt size, accidental selection, and contradictory instructions.
Where should credentials live?
Outside the prompt and model context. Resolve credentials at execution time from an approved secret alias, account, region, and environment.
When should the agent ask for clarification?
Ask when a missing value changes meaning: repository, account, environment, destination, date range, destructive scope, or the identity of the object being changed.
How many retries are appropriate?
Use a small bounded retry budget for transient failures. Validation errors should return to schema inspection; authorization and policy failures should stop immediately.
What should production teams measure?
Track correct-tool rate, valid-argument rate, task completion, human corrections, unsafe-action blocks, latency, cost, provider failure, and citation completeness.
Give Your Coding Agent Real Tool Access
Use QVeris to connect developer automation agents to discoverable, inspectable, and callable external capabilities.